Story thread · 2 reports / 2 sources
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution
thehackernews.com · 7d
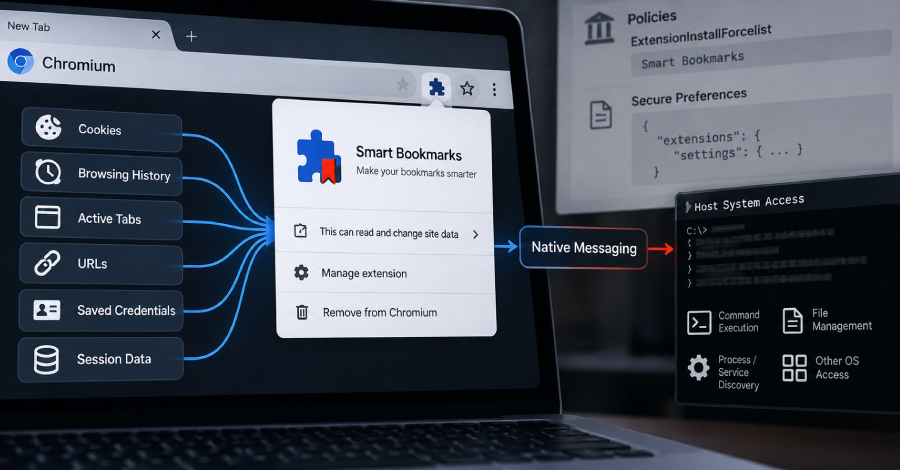
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. "Requiring prior administrative or code execution access, its installer injects the extension directly into Chrome/Edge profiles, bypassing Web Store checks and user prompts by forging Chromium's own Secure Preferences
First report: Le Peep — omaha.com, 9d
The conversation · 0
Sign in to join the conversation.
No comments yet — start the thread.