Story thread · 2 reports / 2 sources
Researchers Use Claude to Port Pre-Auth RCE Exploit From One PLC Model to Another
thehackernews.com · 13d
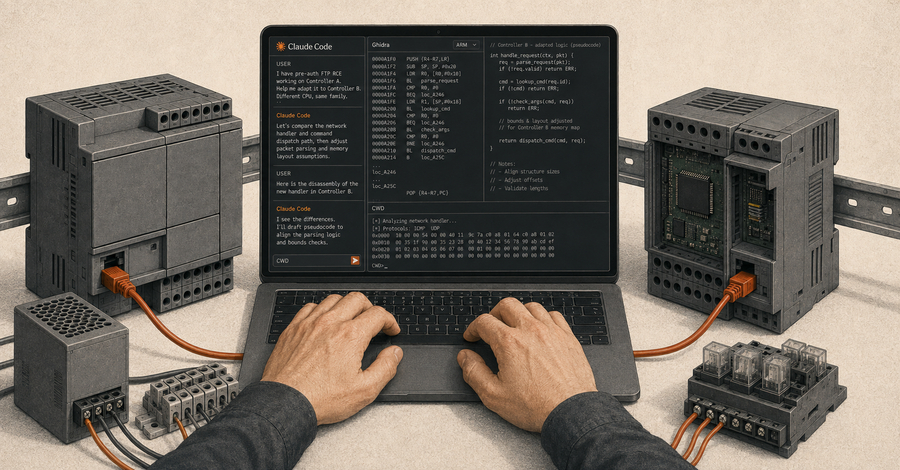
Forescout Research - Vedere Labs said it used Anthropic's Claude to port a working pre-authentication remote code execution (RCE) exploit from one WAGO programmable logic controller (PLC) to another, executing attacker-supplied ARM shellcode on live hardware. The exploit targets CVE-2021-31886, a stack-based buffer overflow in the Nucleus FTP server's handling of the USER command
First report: Experiment: Porting a PLC Exploit With AI Takes Hours and Hundreds of Dollars — securityweek.com, 13d
The conversation · 0
Sign in to join the conversation.
No comments yet — start the thread.